Identity
Access and role control stay inside the appliance
Identity and access review are evaluated with the same system that runs AI.
Inside the IRON MIND appliance, local AI execution, DevRun approval, stage gates, audit evidence, delivery packages, collaboration messaging, and SIEM incident detection run in one operating flow.
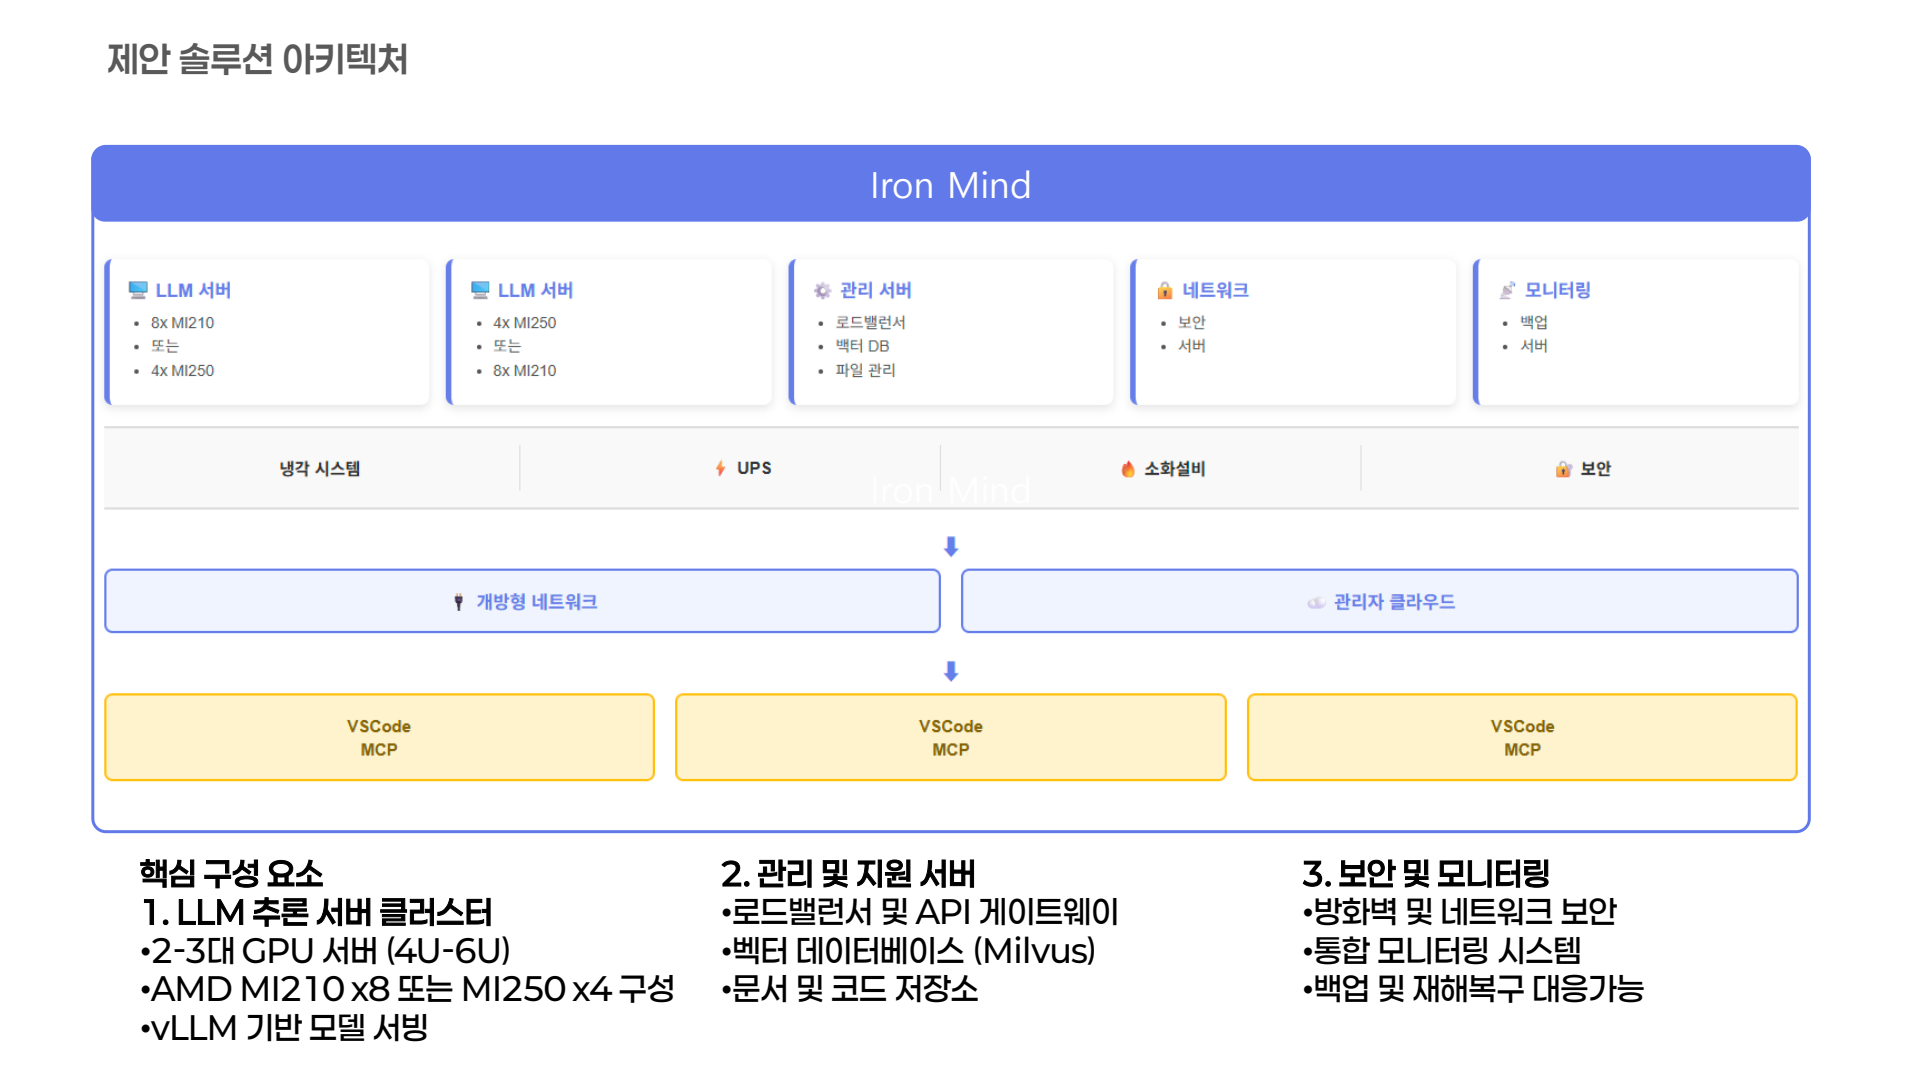
The solution layer is not a separate SaaS tool. It is the control brain that sits inside the appliance.
Role separation, SSO, and project access stay aligned with the control model.
AI runs, artifacts, outputs, and operator context are stored as evidence.
AI use starts inside the appliance instead of an external API path.
Each AI action is linked to artifacts, operators, and project history.
Governance and gate checks happen before submission.
Lower-risk work can move with lighter review while still staying inside the appliance boundary.
Project-critical work keeps evidence and approval checkpoints visible.
High-risk work stays under stronger review conditions and tighter submission control.
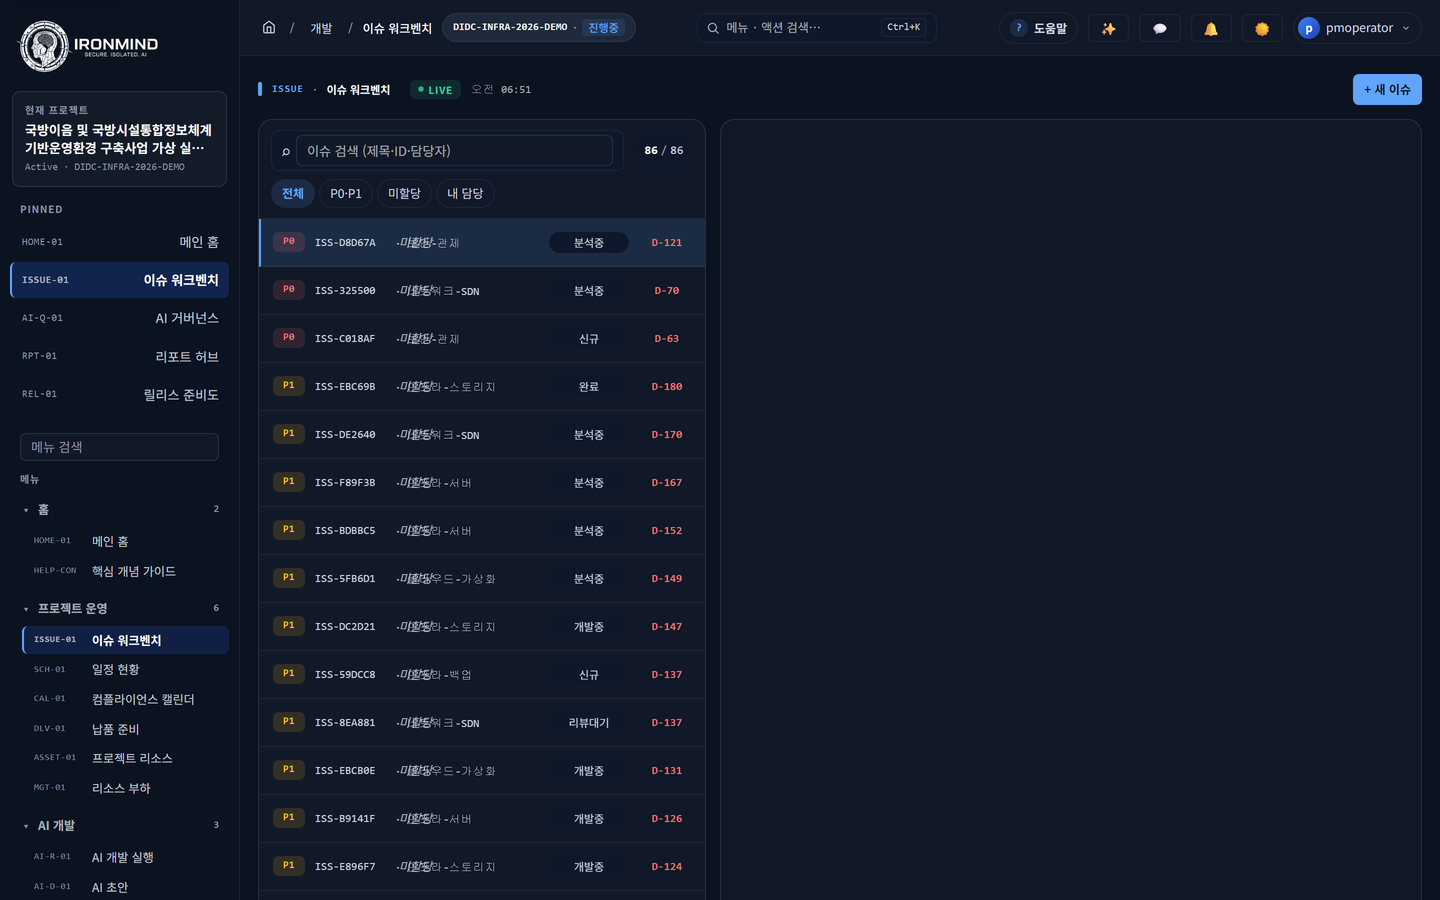
Control decisions become meaningful when issue handling stays connected to project execution.
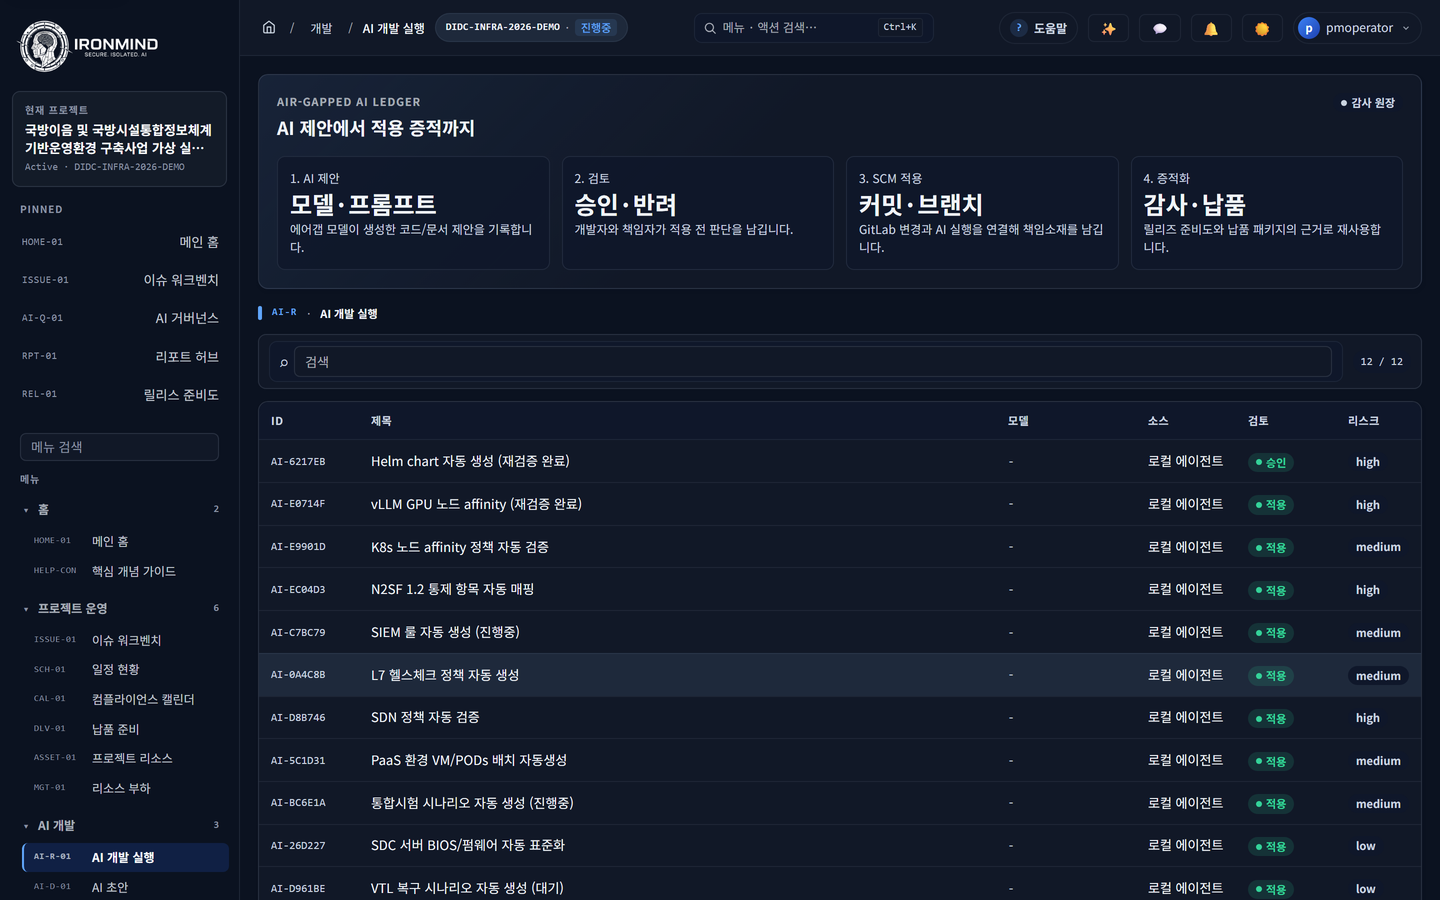
The control layer records AI use as project evidence rather than a disconnected experiment log.
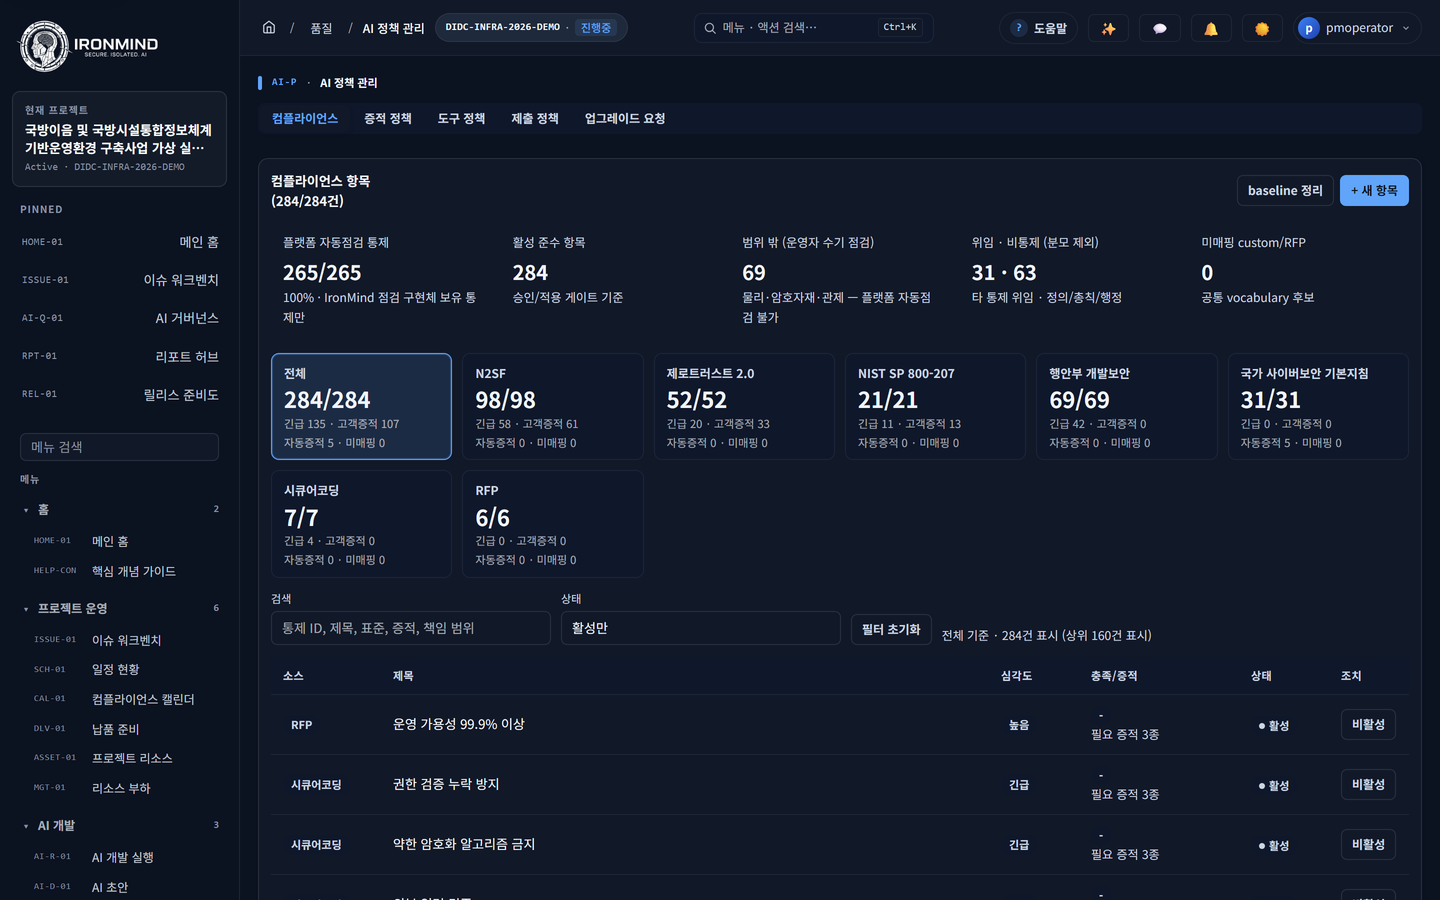
Governance review is visible inside the operating surface instead of a separate spreadsheet.
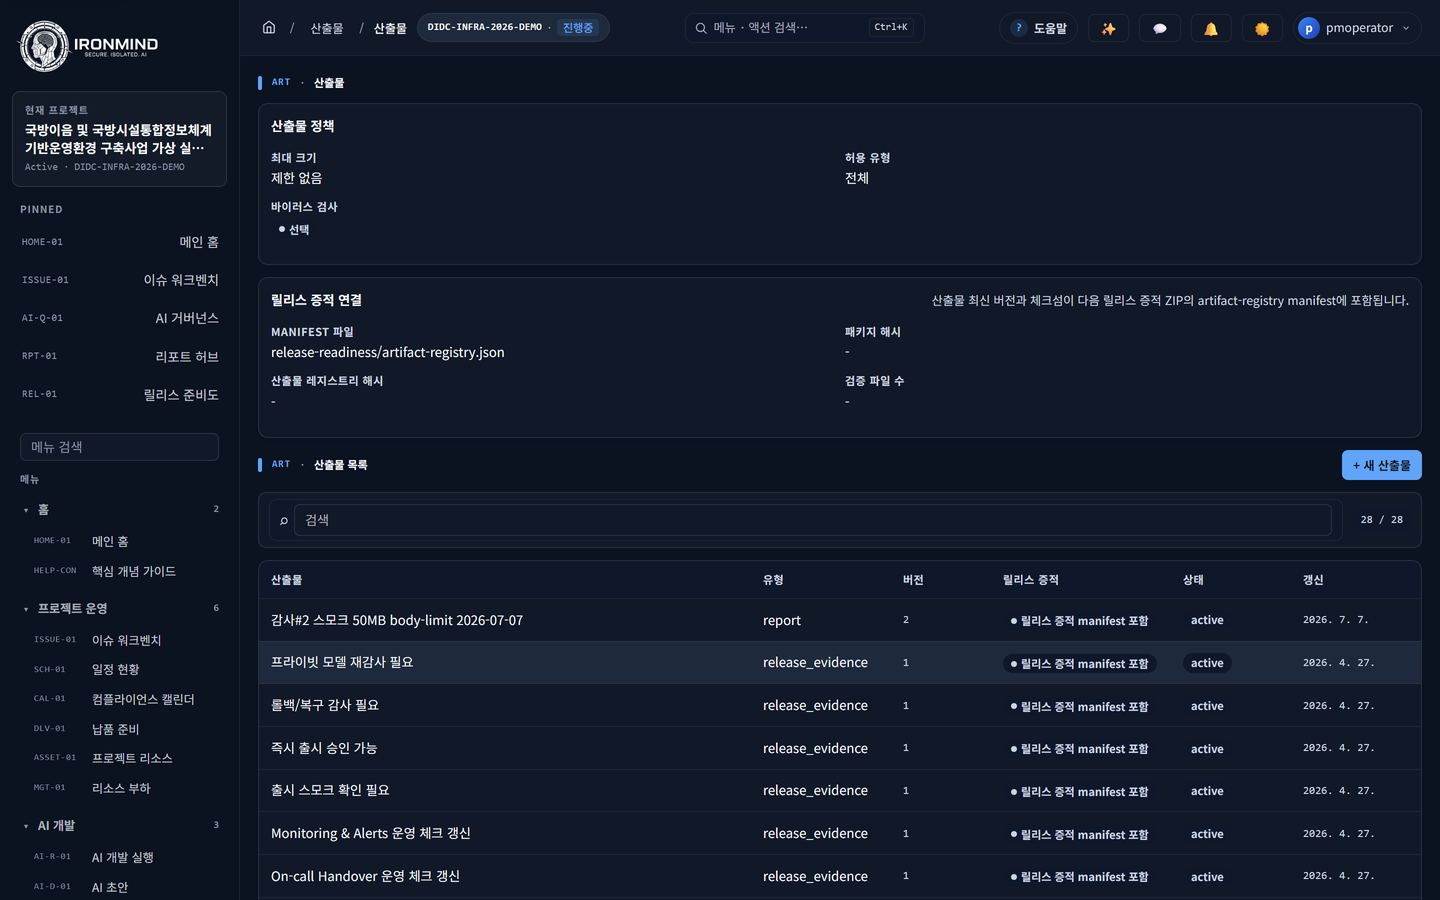
Submission control only works when versions and review state stay visible in the same system.
Evidence Fields
Shows what was asked, generated, and changed in the project.
Shows which exceptions and policy gaps still block the next step.
Shows which milestone still lacks approval and why.
Shows what is ready for review, submission, or audit.
IronMind v1.2.2. Product implementation completeness about 94 / 100, external certifications/audits passed: 0, NIS 12 controls plus mapping/delegation, SIEM, ARIA-256-GCM, mTLS, and 32-container air-gap installation verification.